Saturday, December 7, 2013

Hydra v 7.4: Fast Network cracker

One of the biggest security holes are passwords, as every password security study shows. A very fast network logon cracker which support many different services, THC-Hydra is now updated to 7.4 version.

Hydra available:

 for Linux, Windows/Cygwin, Solaris 11, FreeBSD 8.1 and OSX, Currently supports AFP, Cisco AAA, Cisco auth, Cisco enable, CVS, Firebird, FTP, HTTP-FORM-GET, HTTP-FORM-POST, HTTP-GET, HTTP-HEAD, HTTP-PROXY, HTTPS-FORM-GET, HTTPS-FORM-POST, HTTPS-GET, HTTPS-HEAD, HTTP-Proxy, ICQ, IMAP, IRC, LDAP, MS-SQL, MYSQL, NCP, NNTP, Oracle Listener, Oracle SID, Oracle, PC-Anywhere, PCNFS, POP3, POSTGRES, RDP, Rexec, Rlogin, Rsh, SAP/R3, SIP, SMB, SMTP, SMTP Enum, SNMP, SOCKS5, SSH (v1 and v2), Subversion, Teamspeak (TS2), Telnet, VMware-Auth, VNC and XMPP.

Change Log:
 
New module: SSHKEY - for testing for ssh private keys (thanks to deadbyte(at)toucan-system(dot)com!)
Added support for win8 and win2012 server to the RDP module
Better target distribution if -M is used
Added colored output (needs libcurses)
Better library detection for current Cygwin and OS X
Fixed the -W option
Fixed a bug when the -e option was used without -u, -l, -L or -C, only half of the logins were tested
Fixed HTTP Form module false positive when no answer was received from the server
Fixed SMB module return code for invalid hours logon and LM auth disabled
Fixed http-{get|post-form} from xhydra
Added OS/390 mainframe 64bit support (thanks to dan(at)danny(dot)cz)
Added limits to input files for -L, -P, -C and -M - people were using unhealthy large files! ;-)
Added debug mode option to usage (thanks to Anold Black).Download Hydra Here




Friday, December 6, 2013

[Cansina] Web Content Discovery Application

It takes general available lists of common path and files used by web applications and make URL requests looking back to the server response code. Cansina stores the information in a sqlite database (omitting 404 responses). One for every new url (think this as a kind of projects feature) and the same database for every new payload on the same url.It aims to be (very) simple and straight to use doing only one thing: Discover content.The app is far from being finished, probably is poorly coded and I wouldn't recommend it to use in a serious pentesting session.Lists from fuzzdb are included in this repository for convenience but are not part of the project. You can use whatever list you want.


Features
  • Threads (well, processes)
  • HTTP/S Proxy support (thanks to requests)
  • Data persistance (sqlite3)
  • Support for multiextensions list (-e php,asp,aspx,txt...)
  • Content inspector (will watch for a specific string inside web page content)
  • Skip fake 404 (best as possible)
  • Skip by filtering content
  • Replacing (for URL fuzzing)
  • Reporting tool
  • Basic Authentication
 Download Cansina Here

[zAnti] Android Network Toolkit

Anti consists of 2 parts: The Anti version itself and extendable plugins. Upcoming updates will add functionality, plugins or vulnerabilities/exploits to Anti.

Using Anti is very intuitive - on each run, Anti will map your network, scan for active devices and vulnerabilities, and will display the information accordingly: Green led signals an 'Active device', Yellow led signals "Available ports", and Red led signals "Vulnerability found". Also, each device will have an icon representing the type of the device. When finished scanning, Anti will produce an automatic report specifying which vulnerabilities you have or bad practices used, and how to fix each one of them.


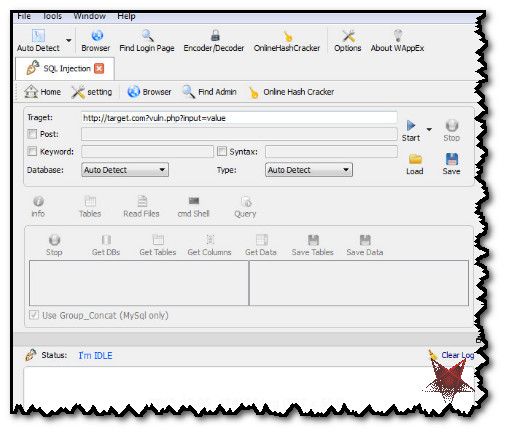
[WAppEx v1.0] Web Application Exploitation Tool

WAppEx is an integrated Web Application security assessment and exploitation platform designed with the whole spectrum of security professionals to web application hobbyists in mind. It suggests a security assessment model which revolves around an extensible exploit database. Further, it complements the power with various tools required to perform all stages of a web application attack.Download Here

Thursday, December 5, 2013

Tutorial Cpanel Hacking/Cracking Tutorial

Cpanel Hacking/Cracking Tutorial:

"Index of /sh3llZ" Upload your shell
while Late Night Browsing Random websites I saw a website with a directory "sh3llz", this directory contain many shells like c99, c100 r57 and others,
it was intresting, i dont know its a Bug or These files was uploaded by any hacker, when I googled it I got Many similar websites
so its Devil's Cafe New exploit, shells already Uploaded and you Can Upload your new one or use and already Uploaded shell and deface the website ..=)

cats.jpg (363×506)


Exploit Title : "Index of /sh3llZ"

Google and Big Dorks :

"Index of /sh3llZ"
"/sh3llZ/uploadshell/uploadshell.php"
intitle:index of/sh3llZ
and you can make own dorks for getting more results =)
Lets Start : Goto Google or Bing.com and type any Dork "Index of /sh3llZ"
"/sh3llZ/uploadshell/uploadshell.php" or intitle:index of/sh3llZ
After Going to Serach result, you will Shell There
Now upload your new shell, or upload Your deface using old shell =) enjoy!!
Must Leave a Comment below to say Thanks !!

Live Demo :

Shell :

http://john.itscool.sx33.net/sh3llZ/uplo...l5c4f3.php
shell password : ..:: Devil's Cafe ::.. (its 404 Not Found Shell Download it here )


Demo Deface :

http://john.itscool.sx33.net/sh3llZ/uplo...klinks.html
(click here to Get Best Deface Pages)

More Shells :

http://sqladminportal.com/sh3llz/
http://phpadmin.org/sh3llz/
http://donate-for-charity.com/sh3llz/
http://php-admin.org/sh3llz/
http://smf-forum.org/sh3llz/
Index of /sh3llZ
Index of /sh3llZ
Index of /sh3llZ
Index of /sh3llZ
http:// blog.dark-action.net/sh3llZ/
Index of /sh3llZ
Index of /sh3llZ
Index of /sh3llZ
http://donate-for-charity.net/sh3llZ/
Index of /sh3llZ
Index of /sh3llZ
Index of /sh3llZ
Index of /sh3llZ
Index of /sh3llZ
Index of /sh3llZ
Index of /sh3llZ
http://donate-for-charity.com/sh3llZ/
http:// Forum.brainshotsblog.com /sh3llZ/
Index of /sh3llZ
http:// john.shots-blog.com/sh3llz/
http:// fisher.active-styles.com/sh3llz/
http:// blog.balcesionlineshop.org/sh3llz/
Index of /sh3llZ

How To Acess Your Shell In JPG

Some time a website have want only image extension
and shell is in PHP so how to upload

First open your shell with notepad and then Save As and change the extension to one of these


shell.php;.jpg shell.php.jpg shell.php..jpg shell.php.jpg shell.php.jpg: ;shell.php.jpg%; shell.php.jpg; shell.php.jpg; shell.php.jpg:;
If you did not find any option for uploading files, but have place where you can add news or new event or something you can use meta http-equiv to make redirection from website to your deface page.Just add this code in news
< meta http-equiv="refresh" content="0;url=http://link_to_your_defacee_page" >
after Getting admin Panel,if you can't upload .php directly upload it with modified extensions as I stated above. After uploading, find the directoey where your fle uploaded, example if you uploaded it in images then it will be in http://website/images/shell.php Sometimes simple extension hiding will not work so you have to use one addon for firefox Live HTTP Headers, Get Live firefox HTTP headers Here https://addons.mozilla.org/en-US/fir...-http-headers/ Install it and then hide shell extension, go to the upload section. Open Live.HTTP Headers and upload shell. Now if you try to go to the link where you have your shell uploaded it will give you error (only on some websites) so we will have to change that hided .php.jpg extension into the.php. So as we uploaded the shell and opened the Live HTTP Headers you should find where you have uploaded your shell.You will have to find the line where ti writes that you uploaded the shell. Select it and then click on button reply. After that you have to find once again the same line of code which shows that you have uploaded shell.So when you find it select the extension you used to hide original.php.In my case it is .jpg (List of all these extension is given in this tutorial at the beginning).When you select it delete it so that we have only c100.php. And after that once again click on reply. It will take you to the shell, and if it does not then you will have to find manually where shell has been uploaded and go to that link. Note : This doesn't work for every website but working in mostly websites

Admin Finder to find Admin login page easily at websites


While hacking a website the most difficult task for a hacker is finding the admin login page of the site where he can input the stolen login Username/Password when he is using SQL Injection. . .

So here we will make their work easier by giving this tool namely AdminFinder! This will search for all suspicious pages on the site and will finally give you the login page!
Get this tool for free from here.Download Here

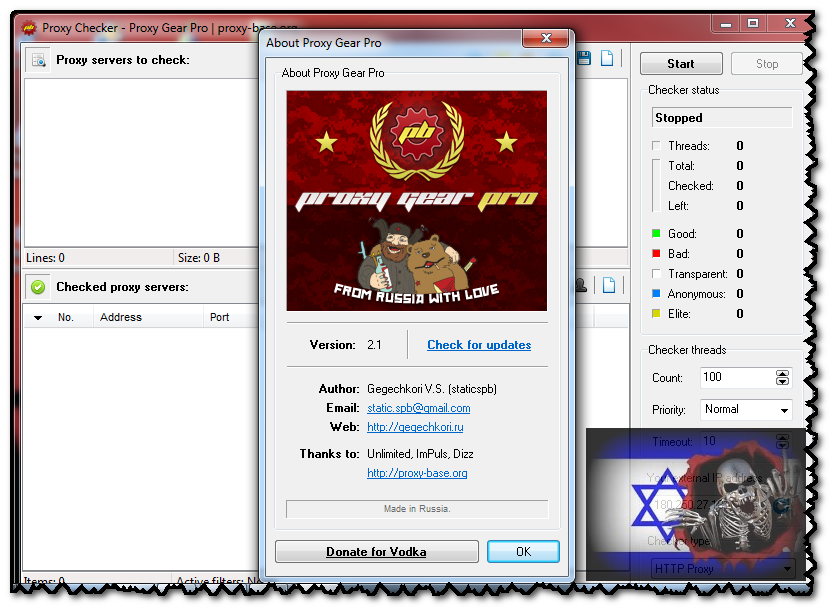
Proxy Gear Pro 2.1

Features:

Easy to use
URL Grabber
High Speed
Adaptive filters
Avtoparser proxies from text / file / URL
The opening of multiple files totaling> 2GB
Identification of the country Proxy
Export lists in whatever mask
Defining proxy timeout
Set up the proxy server directly from the program
Multithreading (up to 1,000 threads and priority control)
Ability to set the connection timeout
Identify the type of proxy (Transparent, Anonymous or Elite)
Work through your own check-server

NEW! Proxy Gear Pro 2.1

* Fixed Google CAPTCHA bug
* Fixed detection of Elite proxy servers
* Added date filter in Google Grabber
* Added antigate.com support for Google Grabber
* Added ability to limit page size in URL Grabber
* Added save button for grabbed proxy in main window
* New parsing algorithm for better speed results
* Clicking on ad-banner now opens default browser
* Minor bugs fixed.Download Proxy Gear Pro Via Box And Sendspace


Subscribe in Bloglines Msn bot last visit powered by MyPagerank.Net Yahoo bot last visit powered by MyPagerank.Net
I heart FeedBurner downtime checker The Ubuntu Counter Project - user number # 31290

 
Twitter Delicious Facebook Digg Stumbleupon Favorites More

 
Powered by TadPole
FOG FLAMES